


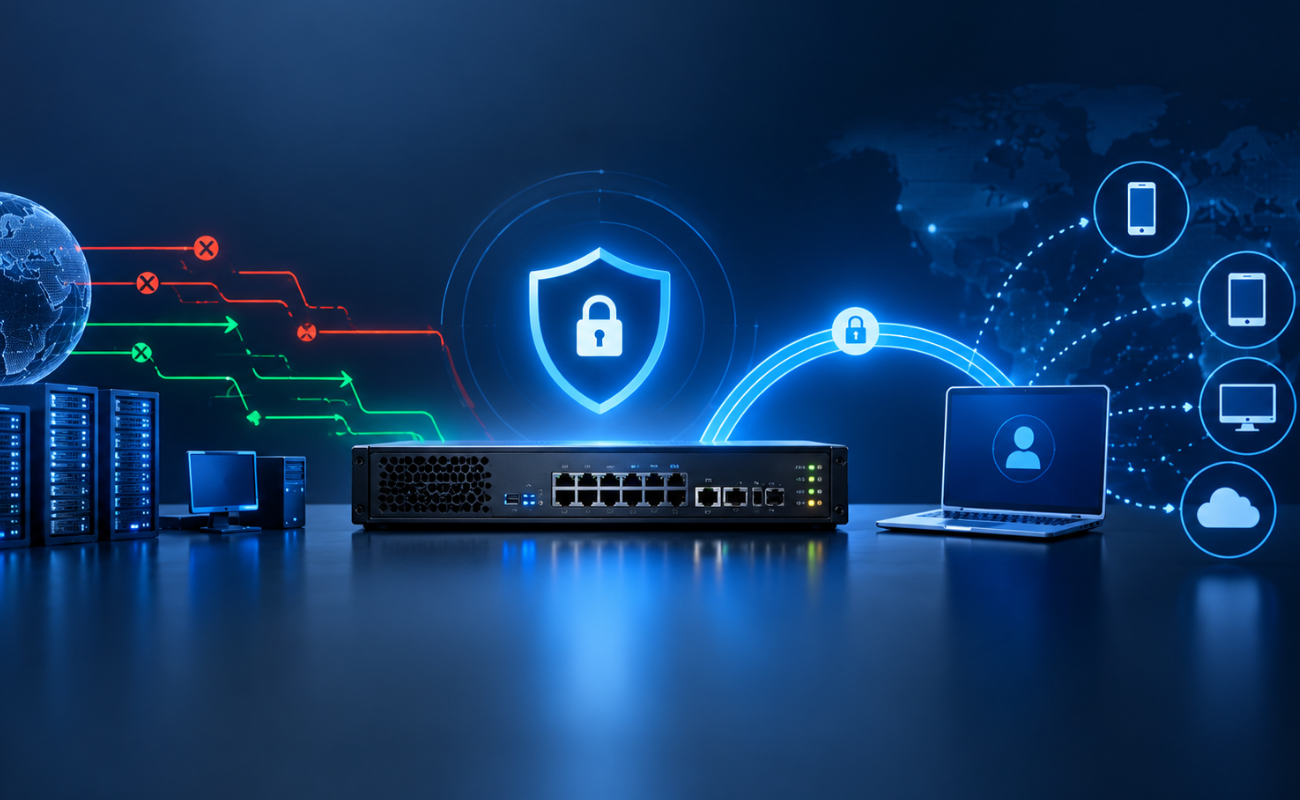
Businesses need reliable network security to protect sensitive information, prevent unauthorized access, and maintain secure communication between employees, servers, and external networks. Two important technologies in this area are VPN firewalls and standard firewalls.
Although both can help protect business networks, they serve different primary purposes. A standard firewall controls network traffic according to security policies, while provides an encrypted connection between users or networks over an untrusted network such as the internet. Some firewall appliances combine both capabilities in one solution.
Understanding VPN Firewall vs Standard Firewall helps businesses choose the right solution for office networks, remote employees, branch offices, and enterprise infrastructure.
In this guide, we compare seven key differences, explain the advantages of each option, and explore when businesses may need both.
1. Main Purpose and Function

The first difference between a VPN firewall and a standard firewall is their primary purpose.
What Is a Standard Firewall?
A standard firewall monitors and filters incoming and outgoing network traffic according to configured security rules. It can allow legitimate connections and block traffic that does not meet the organization’s policies.
Common functions include:
-
Filtering traffic by IP address and port
-
Controlling network protocols
-
Restricting unauthorized connections
-
Separating internal and external networks
-
Logging permitted and blocked traffic
What Is a VPN Firewall?
The term firewall can refer to a firewall appliance that support connections or a firewall configured to protect traffic entering and leaving a tunnel.
Establishes an encrypted connection between a remote user and a corporate network, or between two networks. The firewall can then apply access policies to traffic passing through that connection.
Key difference: A standard firewall primarily controls network access, while functionality provides a secure communication tunnel. A single appliance can perform both roles.
2. Traffic Encryption and Data Protection

Encryption is a major consideration when comparing VPN Firewall vs Standard Firewall solutions.
Standard Firewall
A standard firewall can inspect and filter network traffic, but firewall filtering alone does not automatically encrypt the data being transmitted.
For example, a firewall can block an unauthorized connection to a company server. However, encryption must be provided by the relevant communication protocol or an additional security technology.
VPN Firewall
A uses encryption to protect data traveling through an established tunnel, helping prevent unauthorized parties on the underlying network from reading the protected traffic.
Depending on the implementation, technologies such as IPsec or TLS-based VPNs can protect communications between remote users, branch offices, and corporate infrastructure.
Why It Matters for Businesses
Encryption is especially important when employees connect from:
-
Home offices
-
Public Wi-Fi networks
-
Hotels and airports
-
Remote branch offices
-
External business locations
Key difference: Adds encrypted communication, whereas a standard firewall does not automatically provide -style encryption for all traffic.
3. Remote Access and Connectivity

Remote access is one of the most common reasons businesses deploy technology.
Standard Firewall
A standard firewall protects network boundaries and controls which connections are allowed. However, it does not automatically create a secure remote-access tunnel for employees working outside the office.
Additional remote-access technologies may be needed.
VPN Firewall
A firewall with remote-access capabilities can allow authorized employees to connect to internal resources from external locations.
Depending on the configuration, employees may be able to access:
-
Internal business applications
-
File servers
-
Company databases
-
Remote desktop services
-
Internal management systems
Authentication, access policies, and endpoint security remain important. Connection should not automatically grant unrestricted access to the entire network.
Key difference: A standard firewall controls network traffic, while a remote access provides a secure connection for authorized off-site users.
4. Security Features and Threat Protection

A VPN and a firewall address different security needs, and neither should be treated as a complete security solution by itself.
Standard Firewall
Depending on its type, a standard firewall can enforce rules based on network addresses, ports, protocols, and connection state. More advanced firewalls can also include intrusion prevention, application control, and malware detection.
The capabilities depend on the specific product and its configuration.
VPN Firewall
Adds protection for data traveling through an encrypted tunnel and can help authenticate remote users or network endpoints.
However, encryption alone does not guarantee that the traffic is safe. Malware or unauthorized activity can still travel through a connection if other security controls do not detect it.
A firewall that supports can inspect tunneled traffic after decryption, provided the traffic is routed through the appropriate inspection policies.
Key difference: technology protects communications in transit, while firewall security policies control access and may inspect traffic for threats.
5. Performance and Network Speed

Performance matters when employees use business applications, transfer large files, connect to databases, or access servers remotely.
Standard Firewall Performance
A standard firewall filters traffic according to its capabilities and configured rules. Actual performance depends on the appliance, traffic volume, enabled security services, and network design.
VPN Firewall Performance
Connections require encryption and decryption, which consume processing resources. Performance can also depend on the protocol, encryption algorithms, tunnel count, and endpoint devices.
For businesses selecting a VPN-capable firewall, important specifications include:
-
Firewall throughput
-
IPsec or TLS VPN throughput
-
Maximum concurrent VPN connections
-
Number of supported tunnels
-
Encrypted traffic inspection performance
-
Hardware acceleration capabilities
Some appliances advertise substantially different firewall and VPN throughput figures, so businesses should compare the appropriate measurements rather than relying on one headline speed.
Key difference: Encryption adds processing overhead, so the selected appliance must support the expected encrypted traffic volume.
6. Deployment, Configuration, and Management
The deployment process varies depending on whether the business needs basic network filtering, remote-access VPN, site-to-site connectivity, or an integrated security platform.
Standard Firewall Deployment
A standard firewall is typically installed at a network boundary or between network segments. Administrators configure security rules, interfaces, routing, logging, and access controls.
VPN Firewall Deployment
Capable firewall requires additional configuration for the VPN connection, such as:
-
Protocols and cryptographic settings
-
Authentication methods
-
Certificates or credentials
-
Tunnel endpoints
-
Routing and permitted networks
-
Specific security policies
For site-to-site VPNs, both ends must use compatible settings. Remote-access VPNs also require a suitable client or supported connection method, depending on the product.
Key difference: VPN deployments involve additional tunnel, encryption, and authentication settings beyond ordinary firewall rules.
7. Cost, Scalability, and Business Use Cases
The final difference involves total cost and how well each solution supports the organization’s requirements as it grows.
Standard Firewall
A standard firewall may be sufficient for businesses that primarily need network traffic filtering and access control. The total cost depends on appliance capacity, security features, support, and licensing.
VPN Firewall
Capable firewall can provide both network protection and secure connectivity, potentially reducing the need for separate VPN gateway hardware.
However, costs may include additional licenses, remote-access subscriptions, stronger hardware, authentication services, and ongoing administration.
Which Businesses Need VPN Functionality?
Capability is particularly useful for organizations with:
-
Remote employees
-
Multiple office locations
-
Branch-to-headquarters connections
-
Remote IT administration requirements
-
Business applications hosted on internal networks
Key difference: A standard firewall may meet basic network protection needs, while a VPN-capable firewall adds secure remote or site-to-site connectivity when required.
1. Key Benefits of Using a Firewall in Business Networks
A firewall helps businesses protect their IT infrastructure by controlling incoming and outgoing network traffic. It creates security rules that determine which connections are allowed and which should be blocked.
Key benefits include:
-
Unauthorized Access Prevention: Blocks connections that do not meet established security policies.
-
Threat Detection: Identifies suspicious traffic and helps prevent malicious activity.
-
Access Control: Limits communication between users, devices, and business applications.
-
Network Visibility: Provides logs and reports that help IT teams investigate unusual activity.
-
Business Continuity: Reduces the risk of security incidents disrupting essential services.
Choosing the right firewall depends on the size of the organization, the sensitivity of its data, and the complexity of its network.
2. How Network Segmentation Improves Security
Network segmentation divides a large network into smaller, controlled sections. This approach helps organizations limit communication between departments, servers, applications, and sensitive databases.
For example, a company can separate its employee network from its finance servers and administrative systems. If one device becomes compromised, carefully configured access rules can help prevent the incident from spreading across the entire infrastructure.
Effective segmentation involves:
-
Separating networks according to their purpose and security requirements.
-
Restricting communication to approved services and devices.
-
Applying access rules between network segments.
-
Monitoring traffic for unexpected connections.
-
Reviewing security policies whenever the infrastructure changes.
These measures can reduce unauthorized access and limit the potential impact of a security breach.
3. Essential Firewall Maintenance Practices
Installing a firewall is only the first step in protecting a business network. Regular maintenance ensures that security policies remain effective as devices, applications, and business requirements evolve.
Organizations should follow these practices:
-
Update Firmware Regularly: Install approved security updates to address known vulnerabilities.
-
Review Access Rules: Remove outdated rules and permissions that are no longer required.
-
Monitor Security Logs: Investigate unusual traffic patterns and repeated connection attempts.
-
Protect Administrative Access: Restrict management interfaces to authorized administrators and trusted networks.
-
Test Configurations: Verify that security policies block unauthorized traffic without disrupting legitimate business operations.
-
Maintain Backups: Keep secure copies of configurations to support recovery after failures or incorrect changes.
A consistent maintenance schedule helps businesses improve protection, reduce configuration errors, and maintain reliable network operations.
4. How to Choose the Right Firewall for Your Organization
Selecting a firewall requires evaluating the organization’s current infrastructure and future growth plans. A suitable solution should provide the necessary security capabilities without creating unnecessary complexity or cost.
Consider these factors before making a decision:
-
Network Size: Estimate the number of users, devices, offices, and servers that require protection.
-
Traffic Capacity: Choose hardware that can handle expected traffic while maintaining acceptable performance.
-
Security Features: Evaluate intrusion prevention, application control, content filtering, and centralized monitoring.
-
Remote Connectivity: Determine whether employees and administrators need secure access to internal resources from outside the office.
-
Scalability: Ensure the solution can accommodate additional users, branches, and workloads.
-
Management Requirements: Consider whether your IT team can manage the device internally or needs a centrally managed service.
The best option is one that matches the business’s actual security requirements, supports its network architecture, and can be maintained effectively over time
VPN Firewall vs Standard Firewall: Comparison Table
| Feature | Standard Firewall | VPN Firewall |
|---|---|---|
| Main purpose | Network traffic control | Firewall protection plus capabilities |
| Traffic filtering | Yes | Yes, when implemented as a firewall |
| VPN encryption | Not inherent | Supported through functionality |
| Remote-access connectivity | Requires additional solution is needed | Can support authorized remote access |
| Site-to-site VPN | Not inherent | Can support secure network-to-network tunnels |
| Threat inspection | Depends on firewall features | Depends on firewall features and tunnel inspection |
| Configuration | Security policies and routing | Security policies plus configuration |
| Performance considerations | Firewall processing and inspection | Firewall processing plus encryption overhead |
| Best suited for | Network access control | Network protection and secure connectivity |
Note: “VPN firewall” is not a separate, universally standardized firewall category. The table compares a standard firewall without built-in functionality against a firewall that supports Many modern firewalls provide both.
Can a VPN Firewall Replace a Standard Firewall?
Does not replace the need for firewall policies. A primarily provides secure connectivity, while the firewall controls which traffic is permitted.
A business can use a-capable firewall as its main network security gateway, provided the selected product supports the required traffic volume and security features.
For example, a remote employee might connect to a company’s VPN gateway. The firewall can authenticate the connection, establish the encrypted tunnel, and enforce policies restricting access to specific internal servers.
This layered approach helps separate secure connectivity from authorization and threat protection.
Popular Firewall and VPN Solutions for Businesses
Businesses can evaluate products from vendors such as:
-
Cisco — enterprise network security and VPN-capable firewall solutions.
-
Fortinet — FortiGate firewalls with security inspection and VPN features.
-
Palo Alto Networks — enterprise firewall platforms with advanced security capabilities.
-
Sophos — business firewall solutions with integrated security features.
-
Check Point — enterprise network security and VPN technologies.
Features differ by model, software version, licensing, and deployment. Businesses should confirm throughput, supported protocols, concurrent connections, authentication options, and security inspection capabilities before purchasing.
How to Choose the Right Firewall for Your Business
Before selecting a solution, consider these questions:
-
Do employees need remote access? If they must securely reach internal resources from outside the office, remote-access may be appropriate.
-
Do multiple offices need to connect? Site-to-site can connect separate business networks over public infrastructure.
-
What security features are required? Evaluate intrusion prevention, application control, malware detection, and logging.
-
How much encrypted traffic will the firewall handle? Check VPN throughput, not only ordinary firewall throughput.
-
What authentication is available? Consider multi-factor authentication, certificates, and integration with existing identity systems.
-
Can the solution scale? Account for more users, sites, tunnels, applications, and bandwidth.
-
What is the total cost? Include hardware, subscriptions, support, setup, and ongoing administration.
10 FAQs About VPN Firewall vs Standard Firewall
1. What is the difference between a VPN firewall and a standard firewall?
A standard firewall controls network traffic according to security rules. A-capable firewall adds the ability to establish encrypted connections while continuing to enforce firewall policies.
2. Does a standard firewall encrypt internet traffic?
Not automatically. A firewall may filter traffic without encrypting it. Encryption is typically provided by protocols such as TLS or VPN technologies such as IPsec.
3. Is a VPN firewall more secure?
It provides additional protection for data traveling through an encrypted tunnel, but overall security depends on authentication, firewall rules, software updates, endpoint security, and monitoring.
4. Can a firewall include a VPN?
Yes. Many business firewall appliances include remote-access or site-to-site capabilities.
5. Does a VPN protect against malware?
Encrypts communications, but it does not automatically prevent malware. Additional security controls are needed to detect and block malicious content.
6. Can businesses use a VPN firewall for remote employees?
Yes. A properly configured remote access can allow authorized employees to connect securely to approved internal business resources.
7. Does a VPN firewall reduce internet speed?
It can. Encryption, traffic routing, inspection features, appliance capacity, and connection quality can affect performance.
8. What is a site-to-site VPN?
A site-to-site establishes an encrypted connection between two networks, such as a branch office and a company’s headquarters.
9. Do small businesses need a VPN firewall?
It depends on their requirements. Businesses with remote employees or multiple locations may benefit from VPN functionality, while other organizations may need only basic firewall features.
10. What should I check before buying a VPN firewall?
Review firewall and VPN throughput, supported protocols, concurrent connections, authentication features, security inspection, licensing, scalability, and compatibility with your network.
Conclusion
The VPN Firewall vs Standard Firewall comparison highlights two complementary security functions. A standard firewall controls network traffic and enforces access policies, while functionality establishes encrypted connections for remote users or separate networks.
For businesses that need remote access, branch connectivity, or protected communication over public networks, a VPN-capable firewall can combine these functions in one platform. The right choice depends on network architecture, performance requirements, security policies, budget, and future growth.
You can also explore our guide on 7 Firewall NGFW Types Compared for Business Network Security to compare different firewall technologies and find the right security solution for your business.
Shop now
Sold out

Sold out
Sold out

Sold out
Sold out
Sold out
Related posts
VPN Firewall vs Standard Firewall: 7 Key Differences

Businesses need reliable network security to protect sensitive information, prevent unauthorized access, and maintain secure commu...
Rack Server vs Tower Server: 6 Key Differences Explained

Rack Server vs Tower Server: 6 Key Differences Explained
Choosing between a rack server and a tower server is an important decisi...
SSD vs HDD Storage: 8 Key Differences Every Business Should Know
SSD vs HDD Storage: 8 Key Differences Every Business Should Know
Choosing the right storage technology is essential for businesse...
Router Performance Explained: 7 Factors That Affect Your Internet Speed

Router performance plays a critical role in determining how efficiently a business network handles daily operations. From cloud-ba...
10 Router Security Features That Help Protect Business Networks
Business networks are constantly exposed to security risks, from unauthorized access and malicious traffic to compromised devices ...
Stateful Firewall vs Next-Generation Firewall: 8 Major Differences
Firewalls play a critical role in protecting business networks from unauthorized access, suspicious traffic, and cyber threats. Ho...
7 Firewall NGFW Types Compared for Business Network Security
Choosing the right NGFW firewall is an important part of protecting business networks fro...
11 Server Features Every IT Manager Should Look For
11 Server Features Every IT Manager Should Look For
Choosing the right server is an important decision for any organization. Serv...
Best RAM Options for Performance Workstations
Best RAM Options for Performance Workstations
Modern performance workstations are built for demanding workloads such as 3D render...
Dual-WAN vs Single-WAN Routers: 6 Key Differences Compared
Modern businesses rely heavily on stable Internet connectivity for cloud applications, communication, online platforms, remote acc...
Wi-Fi Router vs Wired Router: 8 Differences Every Business Should Know
Choosing the right networking equipment is an important decision for any business. As organizations become increasingly dependent ...
Storage Buying Guide: 7 Things to Consider Before You Choose
Storage Buying Guide: 7 Things to Consider Before You Choose
Modern businesses generate and manage large amounts of data every da...
